How it works
How it works, starting with the free AWS bill check
A free read-only AWS bill check first, then cuts you approve one at a time. We just keep 25% of what we saved you. What software does, what engineers do.
The short version
It starts with the free AWS bill check, and everything after it is optional. Nothing changes in your systems unless you approve it first, and every action we take is written to a log you can read.
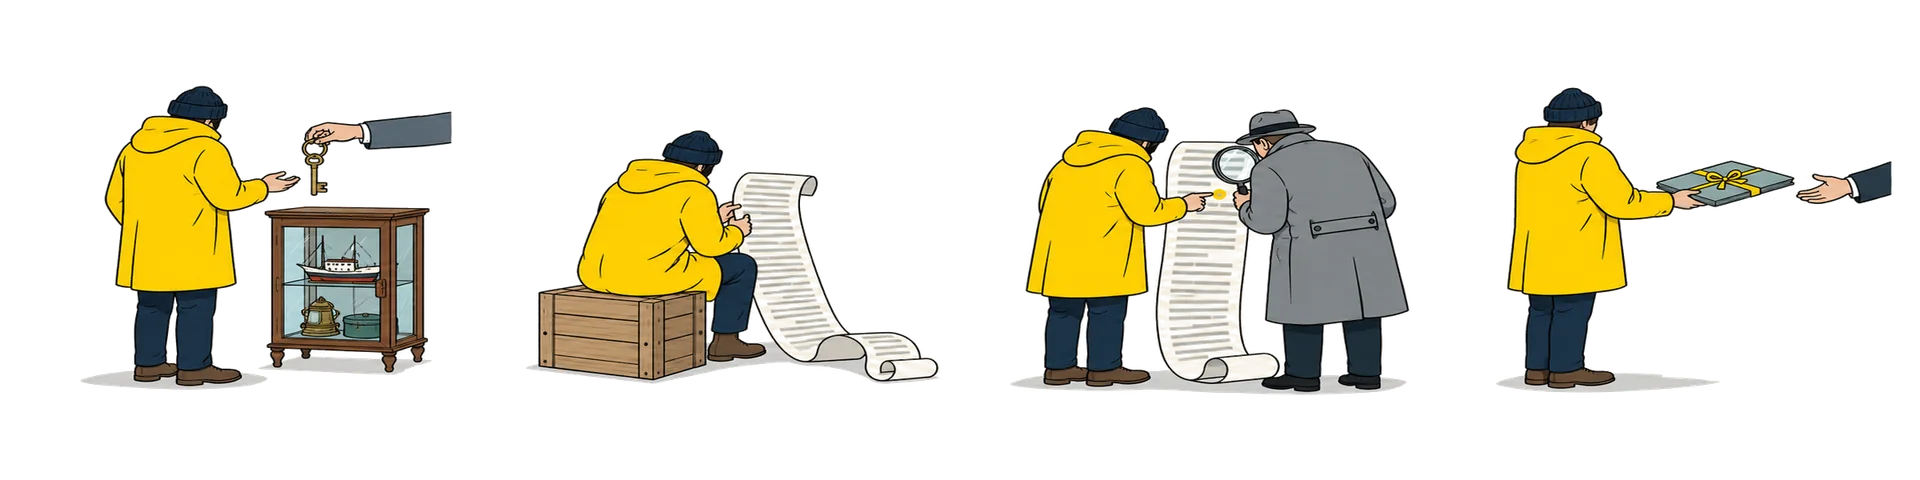
Four steps, and you can stop after any of them
Step 1
Free AWS bill check
Every dollar on your AWS bill you could stop paying, ranked, in dollars. You keep the report.
Free AWS bill checkStep 2
We cut the bill
You approve each change, we make it, and the saving is measured on your real invoice. No savings, no fee.
How the 25% worksStep 3
Free server review for clients
Backups, alerts, old logins and updates, checked the same way. A ranked list you can fix yourself.
The server reviewStep 4
Monthly plans, if you want them
Guard, Watch or Operate keep the fixes in place, so the work stays off your developers.
See the plansStep 1: The free AWS bill check
- You connect read-only access. You run one template in your own AWS account. It creates a read-only role for us. No passwords or keys change hands.
- Software reads every line. Three months of your bill, line by line, plus idle servers, unattached disks, old snapshots, oversized databases, data transfer and the discounts you already hold.
- A senior engineer checks the findings. False alarms come out. Effort and downtime are set for each line. Every dollar is checked against your actual invoice.
- You get the report within 48 hours. Every dollar you could stop paying, ranked, and a list of exactly what we looked at.
- You decide. Make the cuts yourself, ask us to make them, or leave it there. If you leave it, delete the role and we confirm in writing that our access is gone.
More on the check itself: free AWS bill check.
Step 2: We cut the bill
If you ask us to make the cuts, each one comes to you as a short written note first: what changes, what it saves, whether it needs downtime, and how to undo it. We make it after you say yes. Long-term discounts are sized to your lowest month, and nothing is bought until you approve it.
We just keep 25% of what we saved you, measured against your own bill from the three months before we start. Discounts you already have are not counted. No savings, no fee, and our share ends in any month you stop. Full terms on the pricing page.
Step 3: The free server review
Once the savings are live, we review the rest of your setup the same way, free for bill-check clients: whether a backup has ever been restored, who hears about an outage first, old logins and keys that still work, and servers behind on updates. You get a short ranked list. Fix it yourself, or ask us.
Want a feel for it now? The 2-minute self-check asks the same questions in the browser, with no email.
Step 4: Monthly care, if you want it
Before anything changes, we write down what runs where, who owns which access and how each part can be recovered. Then we put the basics in place for your plan: monitoring, backups with a restore test, updates on a schedule, alerts going to the right place. For this we need permission to make changes. You decide how that works (see "Approvals" below), and you can narrow it or take it away at any time.
Depending on your plan, each month includes some of:
- Updates applied on a schedule, tested first
- Backups restored to a test copy, with the time it took written down
- Access reviewed against your current team
- Certificates and domains watched for expiry
- A cost report with unusual lines explained
- Releases and incidents handled (Operate)
You get a short written summary each month: what we checked, what we changed, what we found and what we suggest next.
What the software does, and what the engineers do
| Software does | A senior engineer does |
|---|---|
| Reads your bill and settings and flags anything unusual | Decides whether a flag is real or a false alarm |
| Checks backups, expiry dates, open ports and access lists on a schedule | Sets the risk, effort and downtime for each fix |
| Watches your app from outside and raises alerts | Answers the alert and decides what to do |
| Drafts the change note: what, why, how to undo it | Reviews the change, sends it to you and makes it after you say yes |
| Keeps the log of every action | Signs off the monthly summary |
No automated tool changes your systems on its own. Software is how we stay fast and keep prices low; people make the decisions.
The access model
For the bill check and the server review: read-only. We can read billing, settings, backup status and security settings. We cannot change anything, open your stored files or database records, or create logins or keys.
After you hire us: access to make changes, scoped to what your plan covers. Where your platform allows it, that access is limited to the systems we look after and can be time-limited to an approved change window.
Always: the access lives in your account, under your control. Remove it and our access ends. Details on how we handle access and secrets.
Approvals
Before any change, you get a short written note:
- What changes
- Why
- What it saves or protects
- Whether it needs downtime, and when
- How to undo it
Nothing happens until you say yes. For routine work you can approve a standing rule in advance, for example "apply security updates every Tuesday night after the test passes". You choose which work goes on standing approval, and you can withdraw it at any time.
Nothing changes until you approve it
No change skips a step
The same path for a one-line config tweak and for a database move. Here is change 014, an example.
Written up
What, why, cost, and the way back
You approve
In writing, by the person you named
Backup taken
A fresh copy before anything moves
Applied
At the time you picked
Checked and logged
App tested from outside, note sent
The audit log
Every action we take is logged: who or what did it, when, on which system, and under which approval. You get the log.
On top of our log, actions in your cloud account also show up in your provider's own activity log (on AWS, that is CloudTrail). That log lives in your account and we cannot edit it.
example entries, not a real customer
Response times
We reply to normal requests within one business day on every plan.
On Watch and Operate, alerts come to us first, and we start on them as fast as the plan allows. Operate includes hands-on incident handling. The exact response time for urgent issues on each plan is written into your agreement before you start, so you know what to expect before anything breaks.
We are a small senior team. If you need a large team on call around the clock today, we will tell you, and we are probably not the right fit yet. See not a fit.
Leaving
Plans are month to month with no exit fee. When you stop, you remove our access, we send you the documentation of your setup and the final log, and we confirm in writing that our access is gone. Everything we built lives in your accounts and stays with you.
How we work with your systems
You stay in control
Read-only access first
The free bill check needs read access and nothing else. Nothing in your systems changes.
You approve every change
Each change comes as a short written note first: what, why, and how to undo it.
Your data and billing stay yours
Everything stays in your own account. We never become your billing contact.
Every action logged
Every action we take is logged, and the log is visible to you.
One-click access removal
Delete the access role and our access ends at once, with no penalty.
Month to month
There is no minimum term and no exit fee. Stop at the end of any month.
Your free AWS bill check, in 48 hours
One read-only template. Every dollar you could stop paying, ranked. You keep the report even if you never hire us.
read-only accessno savings, no feemonth to month